Cloud identitySep 2026
Entra IAM Lab
Problem
A user needs MFA enforced, app access through SSO, and a clean offboard when they leave, all in a real Microsoft Entra tenant.
Stack
- Microsoft Entra ID (P2 trial)
- Conditional Access
- SAML (Entra SAML Toolkit)
- OIDC (jwt.ms)
What's proven
- Users, a security group (MFA-Test-Group) and P2 licensing set up
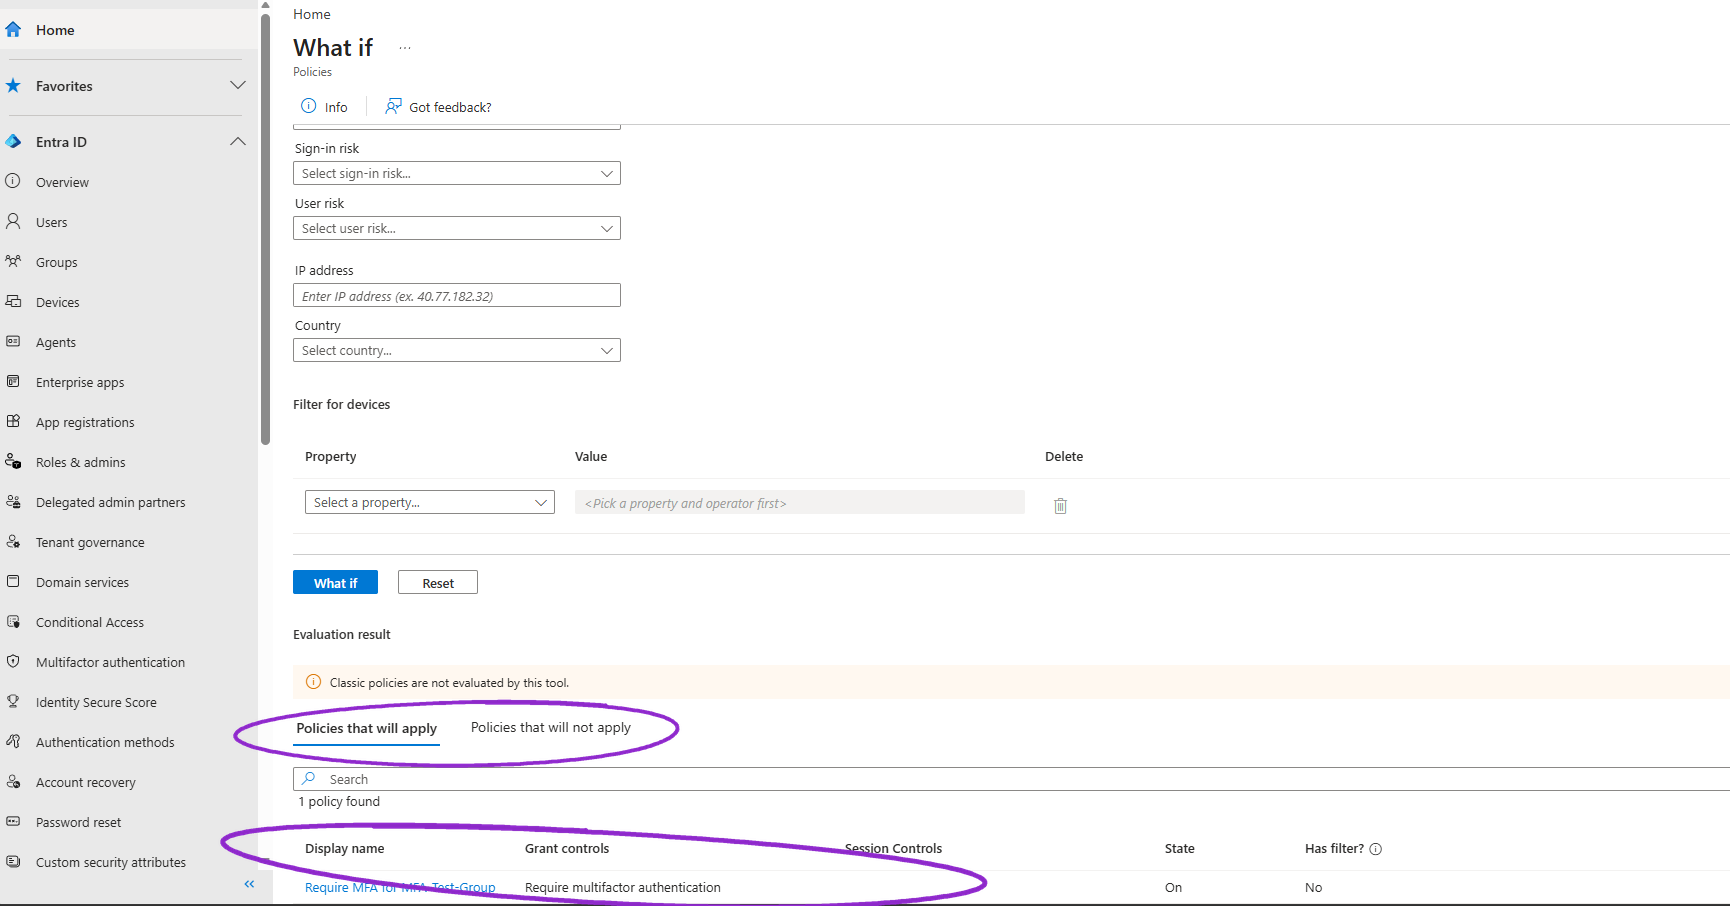
- Conditional Access policy requiring MFA for the group, State On, confirmed with What If
- Leaver disabled, sessions revoked, P2 license removed
- SAML SSO into the Toolkit as testuser; OIDC app with assignment required and an ID token on jwt.ms
In Entra I required MFA for a test group with Conditional Access and gave that group SSO to a SAML app and an OIDC app. For a leaver, I disabled the account, revoked sessions, and removed the license and groups.
View repo and screenshots →
On-prem directorySep 2026
AD User Lifecycle
Problem
Ticket-style joiner and leaver work on a real Windows Server 2022 domain controller.
Stack
- Windows Server 2022
- Active Directory DS + DNS
- ADUC
- VirtualBox
What's proven
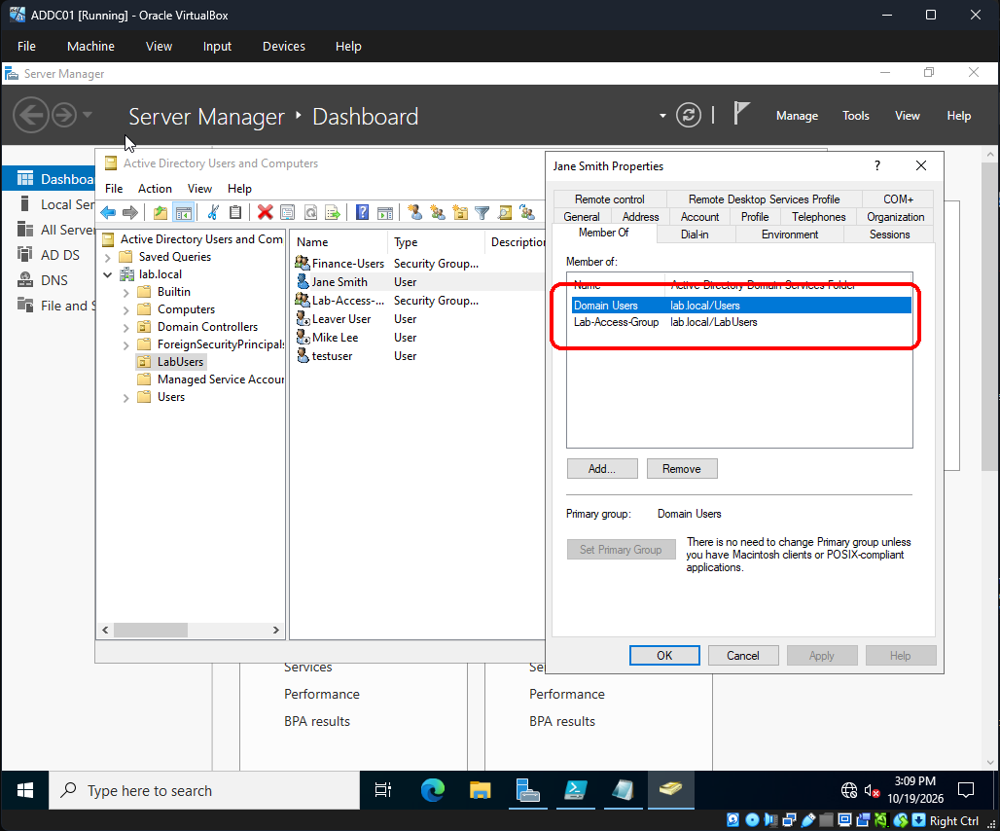
- Promoted DC for lab.local and built OU LabUsers
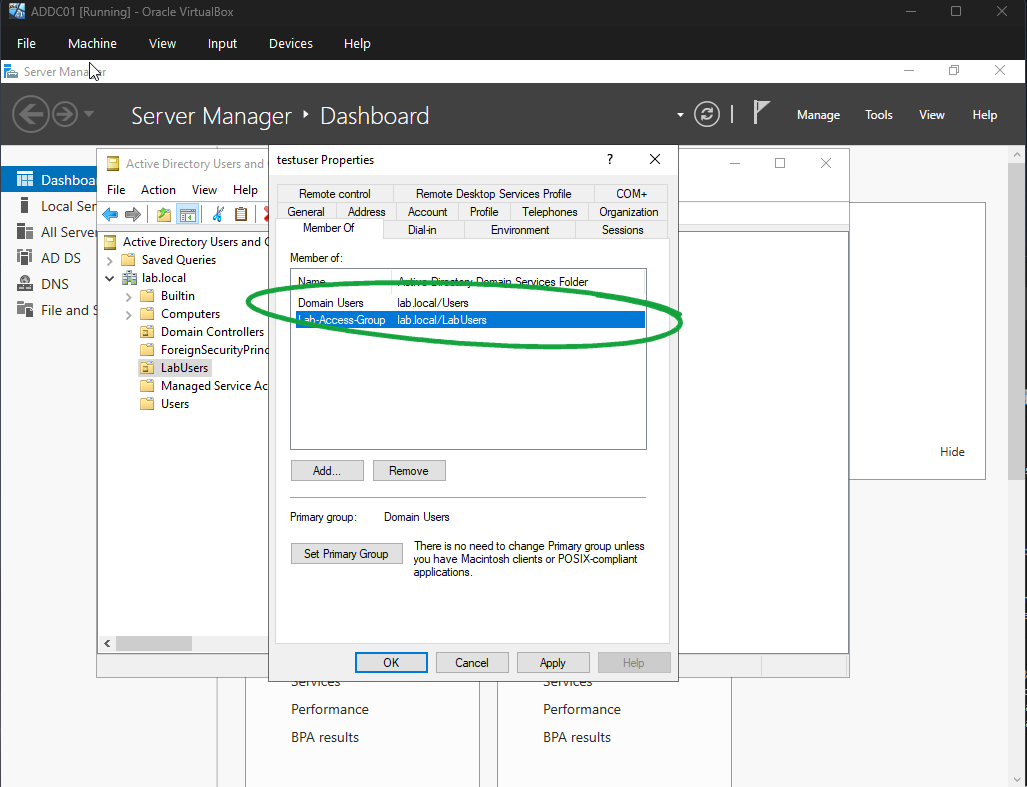
- Created testuser and Leaver User; added testuser to security group Lab-Access-Group
- Proved access from the user side: Member Of → Lab-Access-Group
- Disabled Leaver User (password reset done in the lab, no screenshot shipped)
View repo and screenshots →
SSO / MFASep 2026
Okta SSO / MFA Lifecycle
Problem
Give one user access to a SAML app only through a group, require MFA, then take the access away.
Stack
- Okta Integrator Free
- SAML 2.0
- Okta Verify
- IAMShowcase test SP
What's proven
- Test user created and placed in group SSO-App-Users
- Lab SAML App assigned to the group with Sign On policy Any two factors
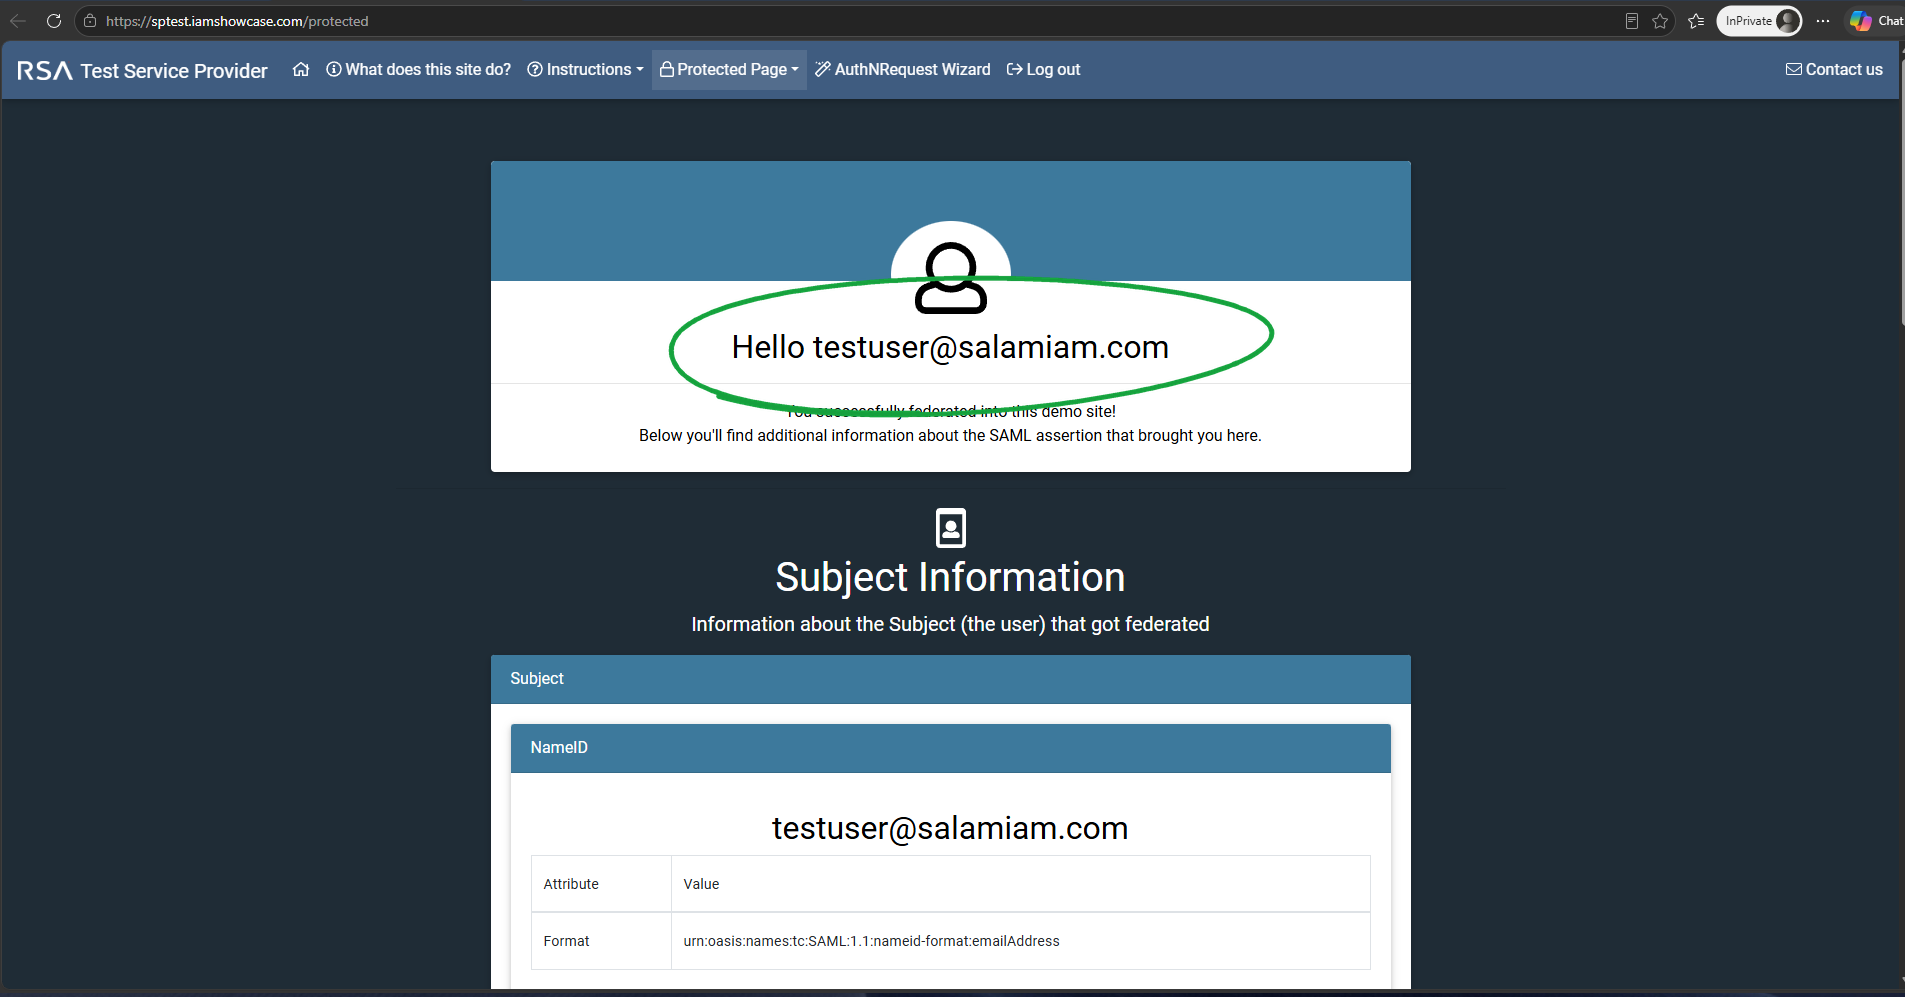
- SSO proof: Hello testuser@salamiam.com, Status Success, Issuer Okta, Audience IAMShowcase
- Revoke: removed from group and the app tile is gone from the dashboard
View repo and screenshots →
Privileged accessOct 2026
CyberArk PAM Self-Hosted 12.6
Problem
A Domain Admin account should only be used with a ticket, an approver, a rotated password and a recorded session.
Stack
- CyberArk Vault / CPM / PVWA / PSM 12.6
- 5 VMs on VMware Workstation
- Active Directory
- PVWA REST API
What's proven
- svc-test (Domain Admins) onboarded into safe Lab-Admins on the WinDomain platform
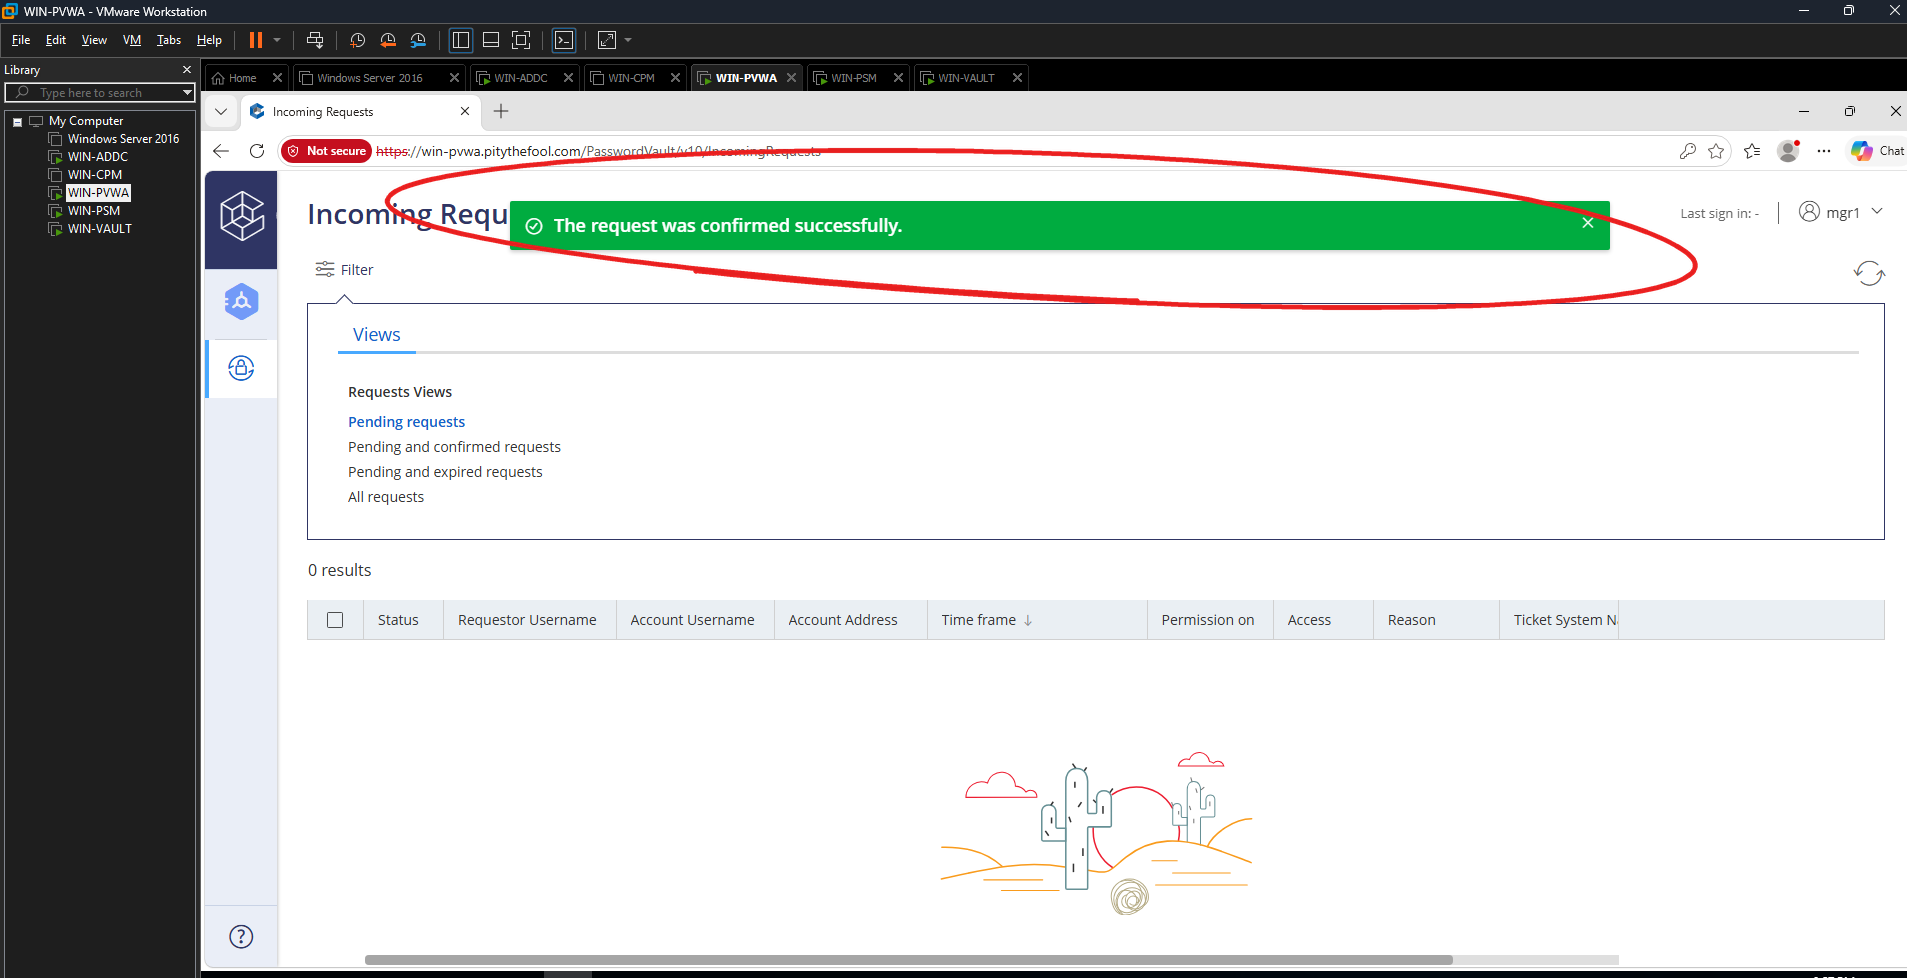
- Requester jdoe and approver mgr1 (separation of duties), dual control in Master Policy; Ticket 1001 requested and confirmed
- CPM rotation failed once (winRc 2245), domain policy fixed, rotated to Compliant
- PSM session to the DC recorded with Activities logged; jdoe removed from Lab-Admins; all 5 VMs snapshotted
View repo and screenshots →
Cloud identityOct 2026
Entra PIM: Just-in-Time Admin
Problem
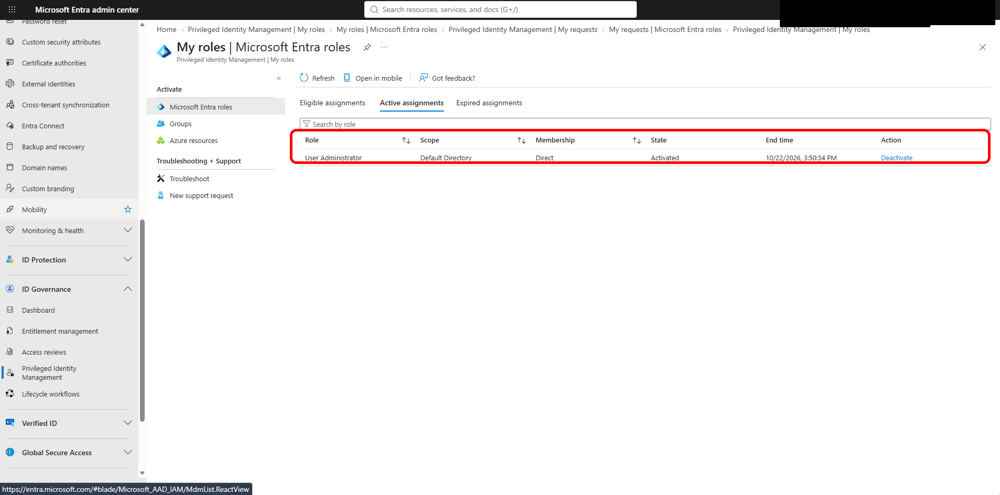
Nobody should hold admin power all the time. I made them ask for it, pass MFA, get my OK, and lose it after an hour.
Stack
- Microsoft Entra ID P2
- Privileged Identity Management
- MFA
What's proven
- Test User made eligible (not active) for User Administrator
- Activation needs MFA, a reason and my approval, max 1 hour
- Request approved, role active, then deactivated (hit the 5-minute minimum rule first)
- Every step shows in the PIM audit log
View repo and screenshots →
Cloud identityOct 2026
ServiceNow Identity Tickets
Problem
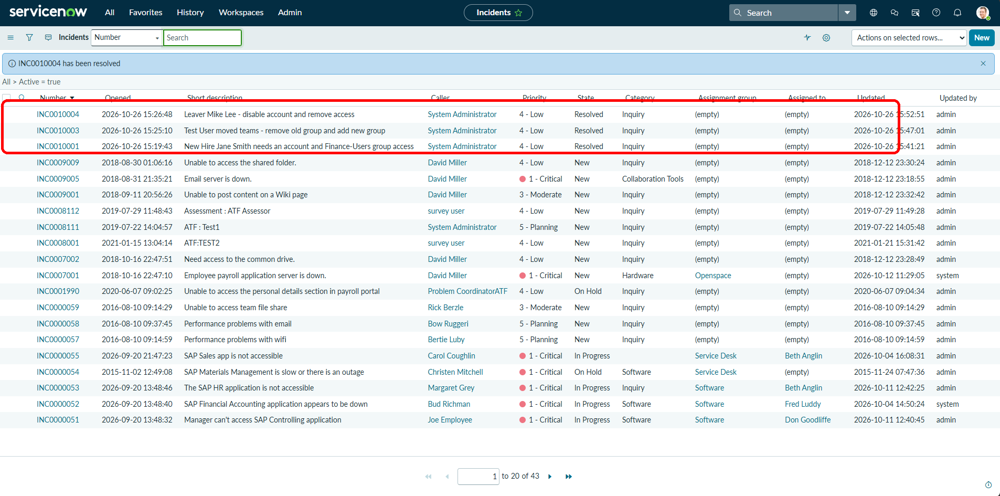
I wanted to work identity tickets the way I would on the job: take the ticket, do the change, write down what I did, close it.
Stack
- ServiceNow developer instance
- Microsoft Entra ID
What's proven
- Three incidents: joiner, mover, leaver
- Each set In Progress, work done in Entra ID, work notes logged
- Joiner created and added to Finance-Users; mover added to Finance-Users; leaver account disabled
- Each resolved with resolution notes
View repo and screenshots →
Cloud identityOct 2026
Entra SCIM Provisioning
Problem
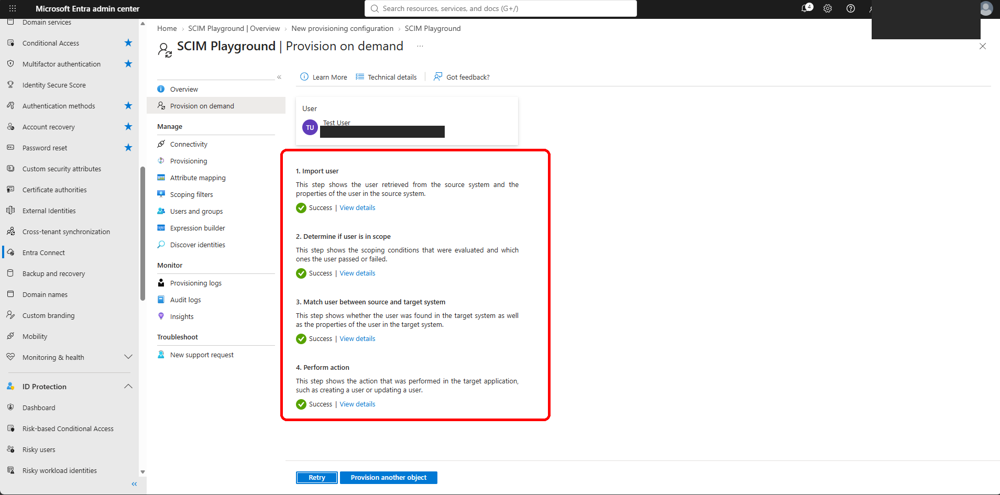
I wanted Entra to build a user's account in an app by itself when I assign them, instead of making it by hand.
Stack
- Microsoft Entra ID
- SCIM 2.0
- scim.dev test server
What's proven
- SCIM connection to scim.dev tested OK
- First provision failed (emails required); added email, retried, user created in the app
- Unassigned user skipped, so scope works
- Leaver is partial: Entra shows IsActive False; app-side deactivation not shown (free test server resets data)
View repo and screenshots →
Cloud identityOct 2026
Entra Access Review
Problem
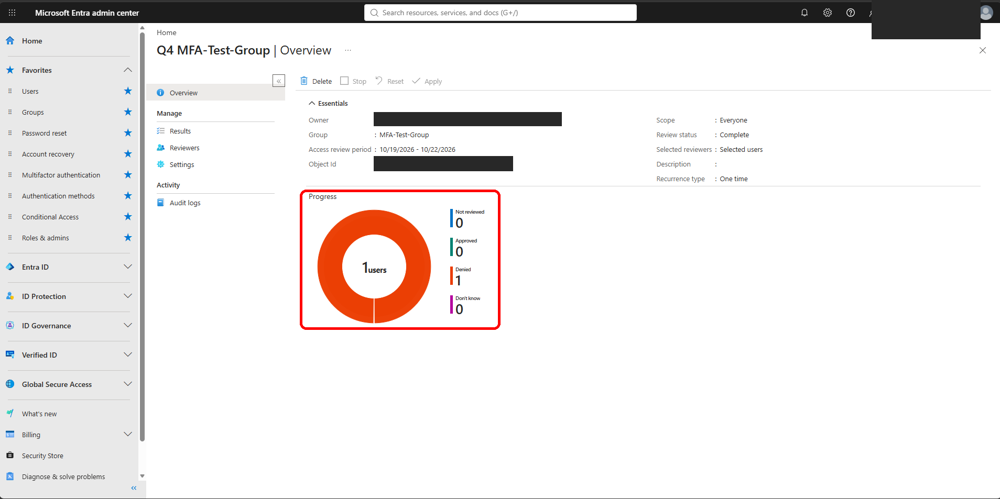
People keep access they don't need anymore. I checked a group and took out who shouldn't be there.
Stack
- Microsoft Entra ID P2
- Access Reviews
What's proven
- One-time review of MFA-Test-Group with auto-apply on
- Test User inactive 30+ days, denied with a reason
- Auto-apply removed them; group shows 0 members
View repo and screenshots →
On-prem directoryOct 2026
PowerShell Joiner / Mover / Leaver
Problem
HR gives me one CSV, I run my script, and every user is built the same way without clicking.
Stack
- PowerShell
- Active Directory module
- CSV
What's proven
- Joiner script created two users in OU LabUsers with a starting group (temp password prompted, not stored)
- First run failed, fixed, re-ran
- Mover: old group removed first, new group added
- Leaver disabled; checked every result in ADUC
View repo and screenshots →
On-prem directorySep 2026
LLDAP Least-Privilege Groups
Problem
A new analyst needs to read, not run the place. No admin unless admin gives it.
Stack
What's proven
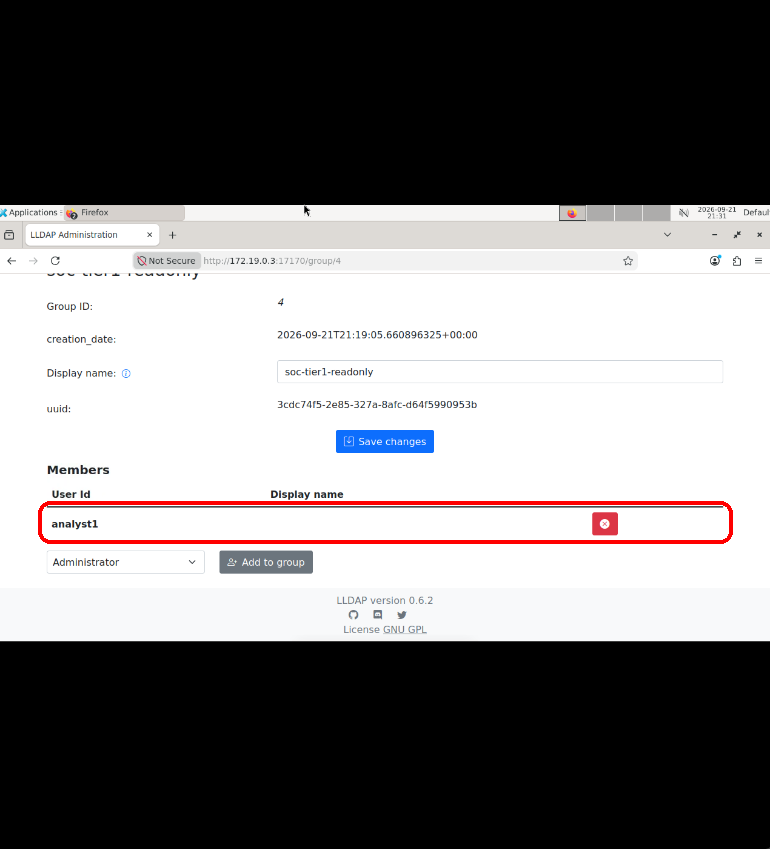
- Created analyst1 and a read-only group
- Kept the admin group admin-only
- Signed in as analyst1 to confirm no admin rights
View repo and screenshots →